A valid credential is not proof of safe intent, the flydubai FZ1073 case suggests
A UAE statement describes a co-pilot already inside the cockpit who attacked his captain, and a security researcher draws design lessons about authority after vetting.
 By
Katharina Brenner
In brief
- The UAE Attorney-General said the co-pilot of flydubai flight FZ1073 attempted a terrorist act, using a crash axe against the captain.
- The person identified by investigators already had legitimate access to the flight deck.
- Researcher Abdulla Saeed Alhebsi proposes second checks and segmented permissions, and rejects profiling.
- Motives and any links remain under investigation.
What the UAE authorities said happened on the flight deck
On 3 October, the Attorney-General of the UAE said that the inquiry into flydubai flight FZ1073 had uncovered a terrorist act attempted by the co-pilot. According to this account, the co-pilot struck the captain with a crash axe in the cockpit and tried to seize command of the plane. The author of an opinion piece published by Daily News Hungary notes that the official statement can be read through the Emirates News Agency, known as WAM.
The General Civil Aviation Authority of the UAE commended the captain, the crew and the passengers, noting that their quick action helped bring matters under control. The author, Abdulla Saeed Alhebsi, who researches security, heritage, risk management and control room operations, sees that reaction as much more than a side detail. He argues that it demonstrates how resilience extends beyond prevention: a system may fail to spot a threat at first and still escape disaster when people grasp their roles, question unusual conduct and step in before authority turns into paralysis.
Work to establish the complete circumstances, the motives and any connections continues. Investigators have not determined a background, an ideology or a network behind the act, and nobody should presume any of them. Alhebsi makes the same point: the confirmed information justifies tougher security questions but does not permit anyone to make up such details.
Already on the trusted side of the door
Alhebsi writes that the individual named by investigators did not break through a protected door. That person already stood on the trusted side of it, holding legitimate access. He contends that for years security has grown very skilled at deciding who is allowed into sensitive spaces. In his words, the tougher question is how to respond when the level of risk shifts after legitimate access was already given.
That is the core of his argument. In industrial settings, he says, a badge or administrator account is often handled as a binary fact, valid or invalid, while real risk is rarely so tidy. A valid credential therefore establishes that someone may enter or act, but it does not by itself show what that person intends to do.
Design safeguards the author proposes
Alhebsi sets out a design principle which, he says, reaches well beyond aviation: the greater the consequence of an action, the more uneasy organisations should be about irreversible authority held by one person. The measures he suggests are:

- an additional human check for high-consequence actions;
- temporary review when behaviour is unusual;
- segmented permissions;
- a rehearsed transfer of control;
- a protected channel allowing colleagues to question something that seems out of place for the task, or to halt an unusual action without having to prove first that the intent is malicious.
He describes these measures as undramatic, which he says is precisely why they can work. They are his proposals, and nothing in the case shows that any of them would have prevented the incident on FZ1073.
He rejects lasting suspicion as well. Aviation, energy, mining, banking and government, he writes, cannot operate if each trusted professional is regarded as a possible offender. As he puts it, trust is a practical necessity, yet trust and authority differ. Someone can remain trusted while a single action warrants a second look, a credential can remain valid while circumstances justify a short-term restriction, and a colleague can voice a concern without accusing anyone.
Why the question reaches Hungary and the Gulf
Alhebsi links the lesson to Hungary, where manufacturing, logistics and transport networks rely on skilled staff who need extensive access to complex systems. He says the UAE faces the same situation in aviation, ports and energy. As he reads it, FZ1073 recalls that the hardest security question arises once vetting has done its job and a professional has lawfully entered the system.
He concludes that Hungary and the UAE each have good reason to safeguard professional trust, and that the way to do it is to keep authority in proportion to the action taken rather than to make trust permanent.
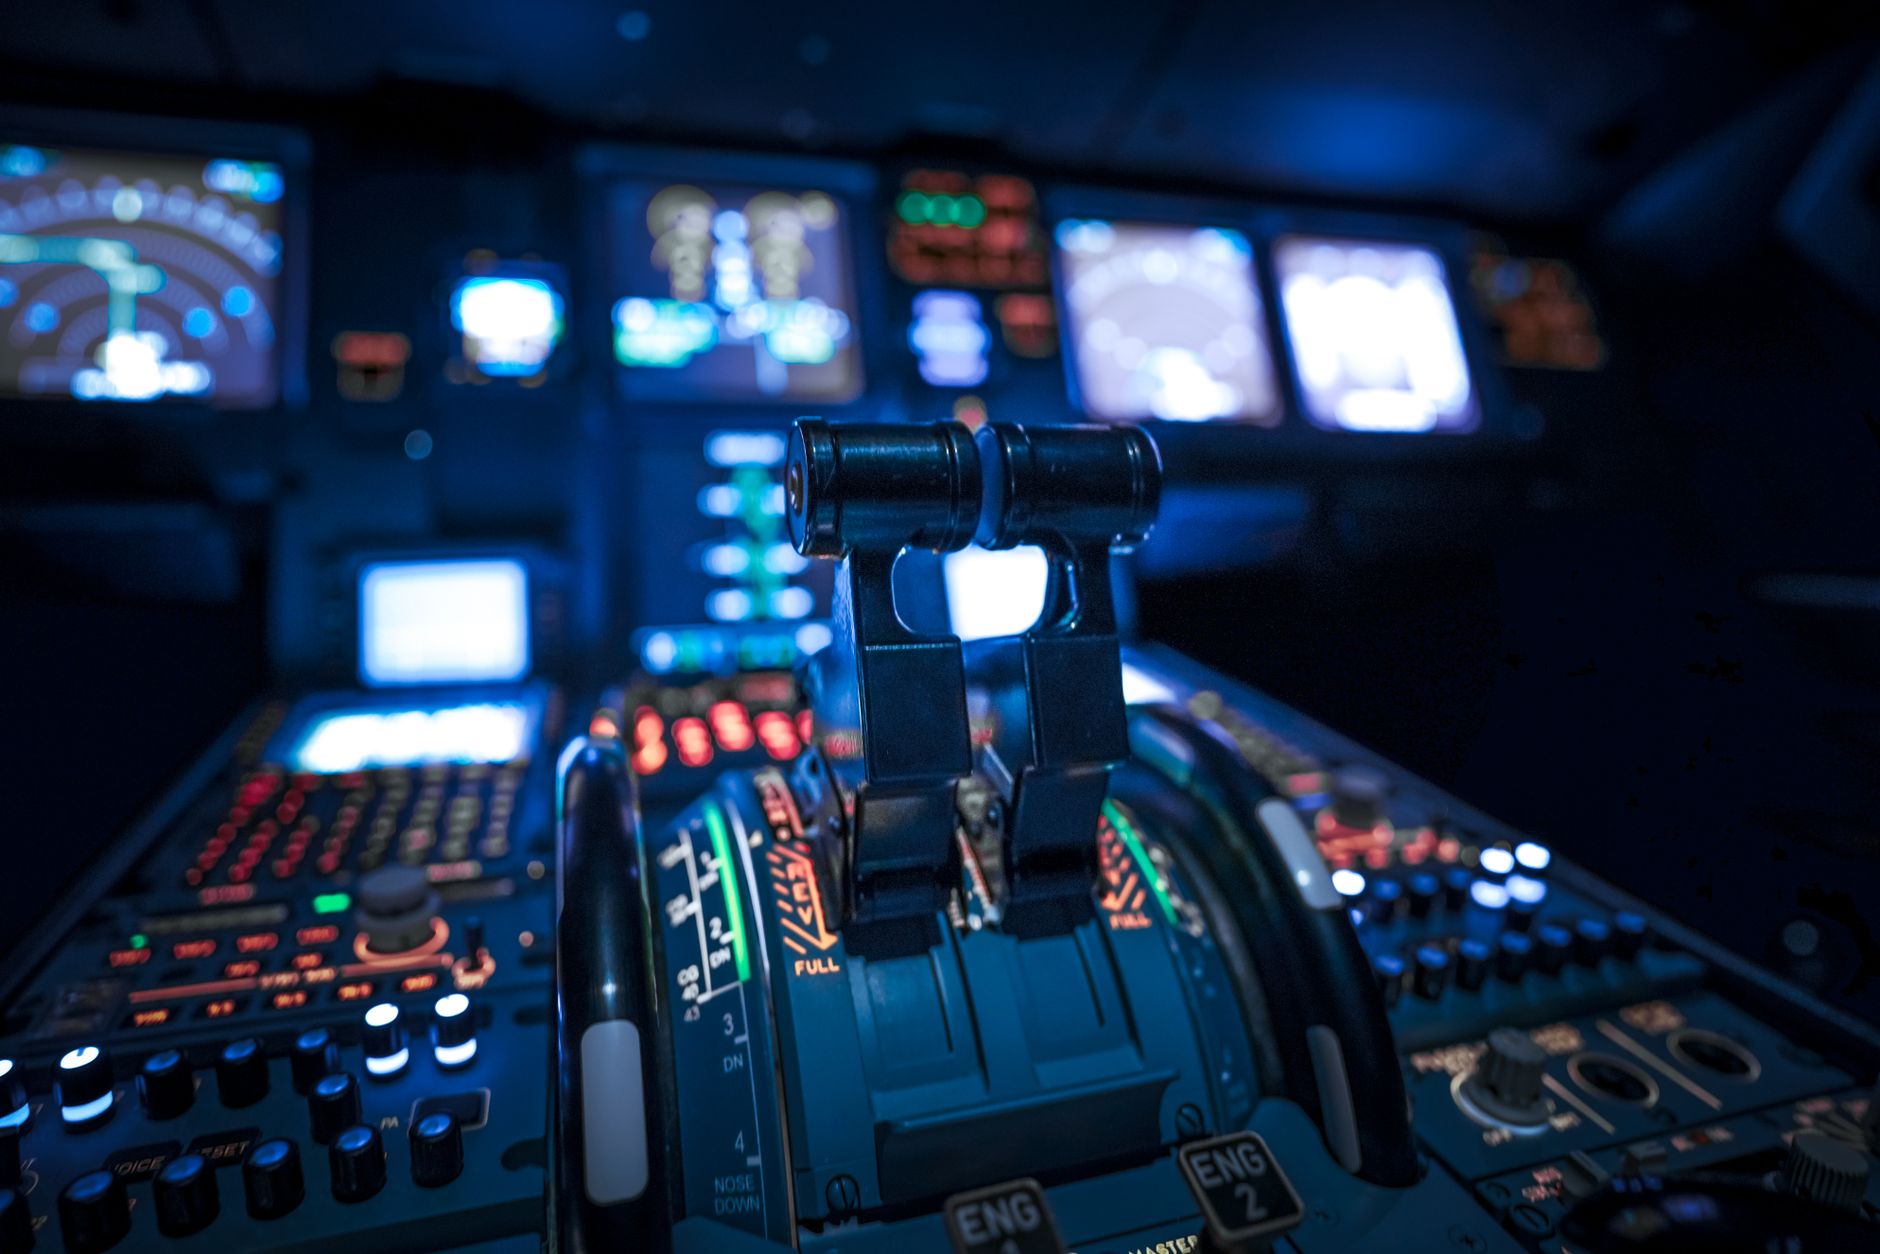
Featured image. Source: Pexels. Credit: Terrence Bowen. License: Pexels License.
Continue reading